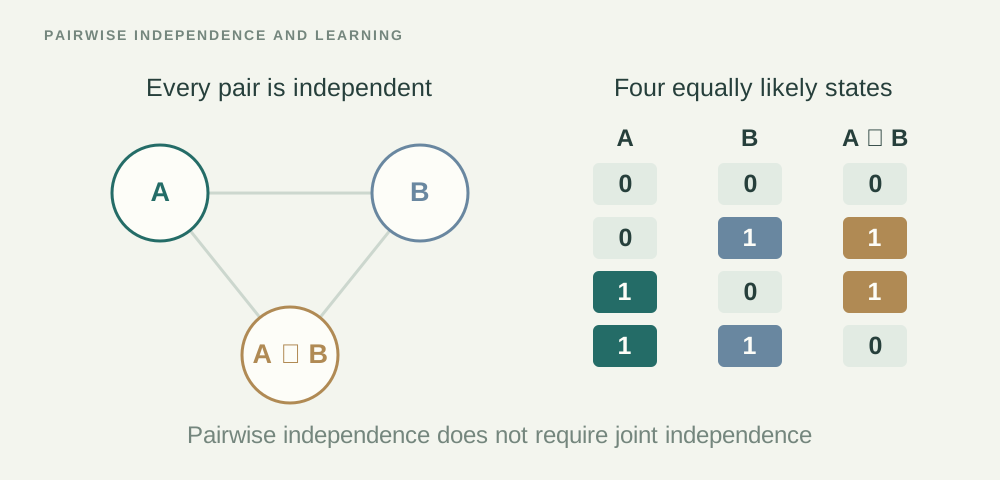
A, B, and A ⊕ B give an exact toy example of pairwise-independent outputs: every pair is uniform, although the triple is constrained. This illustrates the independence property behind the paper’s analysis of gradient information. Research source
About this paper
Studies how almost pairwise independence limits the information available to gradient-based learning attacks.
Gradient variance bounds explain why certain cryptographic function classes are difficult to learn under regular parameterizations. Experiments with Learning with Errors mappings explore how the theory appears during training.
Citation
BibTeX
@article{takhanov2024pairwiseindependence,
  title = {Almost pairwise independence and resilience to deep learning attacks},
  author = {Takhanov, Rustem},
  year = {2024},
  journal = {IACR Communications in Cryptology},
  url = {https://cic.iacr.org/p/1/3/32}
}